PrimusCredence
Provable security for applications — a new field beside your AppSec tools

Who can reach what inside your application — proved, not assumed.

The cloud base is already formally proven. The application on top of it, its plugins and the seams between are not. We prove three things there — who may do what, what traffic can reach where, and where regulated data can go — and return either a proof, which is a strong compliance statement, or the exact request, path or chain that breaks it. Then we help your developers fix it, and re-prove.

For platform & AppSec teams, ISVs, private enterprises and government in the UAE and GCC — and for the MSSPs, consultancies and auditors who serve them.

The same class of automated reasoning the hyperscalers use to verify their own platforms — applied to the layer above it.

Where the risk lives

The base is proven. The app, and the seams, are not.

Plugins & extensions 1
run inside the app — inherit its privilege
Application unproven 1
its own roles, tokens & config — OWASP #1 & #2
The seam
1access via APIs 2network paths 3data paths & copies
Cloud & infrastructure proven ✓
VMs · databases · queues · storage · IAM · network
The hyperscalers formally proved the cloud base. The application above it was never proved — and the seams between can quietly undo it.
→ that gap is what we prove
One method — three services

Access control, network isolation, data residency.

Each service answers one question over every case the model allows. In a demo we show the findings below, then the fix, then the proof.

Access control

Application Access-Policy & Entitlement Verification

Who may do what.

Every app role, token, plugin route and public user — decided over all requests.

Can any app role, API token, plugin route or public user reach data it must not — through the app or its cloud role?

In the demotools run first; none decides these
  • VIOLATEDTwo allowed steps, one breach

    Each step is allowed on its own; together they cross tenants.

  • VIOLATEDA plugin side door

    A plugin route bypasses the app’s own checks.

  • VIOLATEDThe app ↔ cloud seam

    The app’s cloud role lets data cross tenants.

  • PROVEDAfter each fix

    Every user, every request.

Checked whenever access settings change — before anyone can use the change.

Reads the app’s roles, permissions and routes, and its cloud role — read-only.

Network isolation

Network Reachability & Segmentation Proofs

What traffic can reach where.

Routes, security groups, firewall and Kubernetes rules — every path between zones.

Does any path exist from an untrusted zone to this one — and does east-west segmentation actually hold?

In the demotools run first; none decides these
  • VIOLATEDOne policy, every zone pair

    From the cloud into OT, hop by hop — each rule and its owner.

  • WOULD VIOLATEA change, before approval

    A pending firewall rule would open paths into OT.

  • VIOLATEDA one-character slip

    Any workload reaches another tenant’s database.

  • PROVEDEvery row, after the fix

    No packet sent.

No scanning window, no production traffic — safe on OT, and re-run on every change.

Reads device configurations and cloud network descriptions — no packet sent.

Data residency

Data Residency & Sovereignty Proofs

Where regulated data can go.

Backups, replicas, keys, caches — not where data is, but where it can go.

Can regulated data leave the country or the organisation — or could anyone make it leave?

In the demotools run first; none decides these
  • AT RISKNothing has left — yet

    An operations role could move the data outside the organisation.

  • VIOLATEDCopies abroad

    A backup and edge caches sit outside the country.

  • OUTSIDE MODELApplication egress

    Shown, not hidden: the app can reach the internet.

  • PROVEDAfter the fix

    For storage, keys and edge.

Not where your data is — where it can go. Today, and whatever anyone could set up.

Reads cloud access, organisation, storage, key and CDN policies — read-only.
Every service endsin a proof — or the exact request, path or chain that breaks it.
What comes back

Not a score. The exact thing that breaks it.

Every finding is concrete and reproducible on your own systems — and every fix is re-proved.

1 · The requestAccess control
  • Who — the user, role or token
  • What — the action and the record
  • Why — the setting or change that allowed it
  • How far — every user and record affected
PROVEDafter the fix: every user, every request.
2 · The pathNetwork isolation
  • From which zone, to which
  • Hop by hop, across cloud and on-premises
  • The rule at each hop, and its owner
  • Found from configuration — no packet sent
PROVEDafter the fix: every zone pair, required paths kept.
3 · The chainData residency
  • Which regulated store
  • The mechanism that could move it
  • Who could set that mechanism up
  • Where the data would end up
PROVEDafter the fix: storage, keys and edge.
How it works

Detection shows what is happening. A proof shows what cannot happen.

01

Learn

We learn the app’s logic and turn it into a logical model.

02

Define

Its desired security properties become formulas.

03

Solve

Automated solvers decide every case.

04

Report

A proof — or the attack, a fix and a re-proof.

AI assists every step · the expert owns the spec
PROOF

No violating state exists — over the entire space, under a stated model. Not “none was found” — a strong compliance statement.

COUNTER-EXAMPLE

The exact request, path or chain that breaks it — reproducible on your systems. We demonstrate the attack existing tools miss, help your developers fix it, and re-prove.

Not every property is decidable, and a proof holds only for the property and model stated — both are written down. Industrial practice: AWS · Microsoft · Meta · Airbus.

Preventive evidence, beside your testing and your SOC. We add to your stack; we don’t replace it.

For MSSPs, consultancies & auditors

We do not certify — so you have a channel, not a rival.

The commercial move
  • Proof inside bids you already win
  • Recurring: re-proven on every change
  • You keep the client and the contract
Why it deploys easily
  • Read-only access, nothing installed on any host
  • No scanning window, no production traffic
  • Verdicts can land in your SIEM and tickets
  • AI runs in your tenancy; data stays in-region

We produce the technical evidence. Your assessor keeps the opinion.

One analysis, read by engineering, risk and audit — each in its own terms.

First lineEngineering & security operations

The property, its model and assumptions, and either the proof or a reproducible attack path.

Second lineRisk

Likelihood moved off a qualitative guess, with residual risk and the model’s limits stated.

Third lineInternal audit & compliance

A clause-mapped control assertion: objective, status, owner and re-verification date.

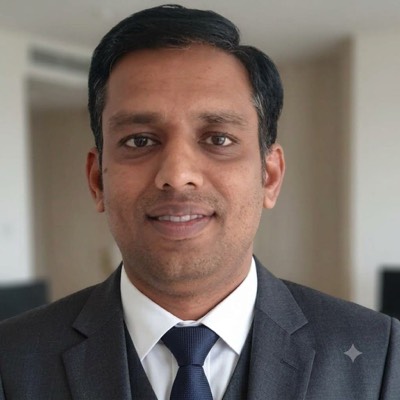
Portrait of Dr. Raghavendra Ramesh, founder of PrimusCredence

Dr. Raghavendra Ramesh

Founder & CEO

Twenty-two years applying mathematical methods to the security and correctness of real systems — a PhD from IISc Bangalore in model checking for information-flow security, Java vulnerability detection at Oracle Labs, and consensus verification at ConsenSys and Supra.

Static analysis · theorem proving · model checking  ·  Dafny · TLA+ · IVy · Lean · Isabelle
Start here — Micro Assessment of Service 1

Let us prove one property on your systems.

One narrow, high-risk slice. Read-only access, nothing installed, weeks not months — and a counter-example on your own systems, or a proof.

Would rather see it first? Book a demo of any service.

General enquiries ·